Bastionskill Scans AI Agent Skills for Malicious Code
A new tool called Bastionskill hit Hacker News as a Show HN, and it's aimed at a problem that's getting harder to ignore: AI agent skills can hide malicious code. The tool scans an agent's skill package before you load it, looking for anything dangerous. That matters because agents are now pulling third-party skills the same way browsers pull plugins, and nobody wants a prompt injection or a data-stealing function hiding in one.
What is Bastionskill, exactly?
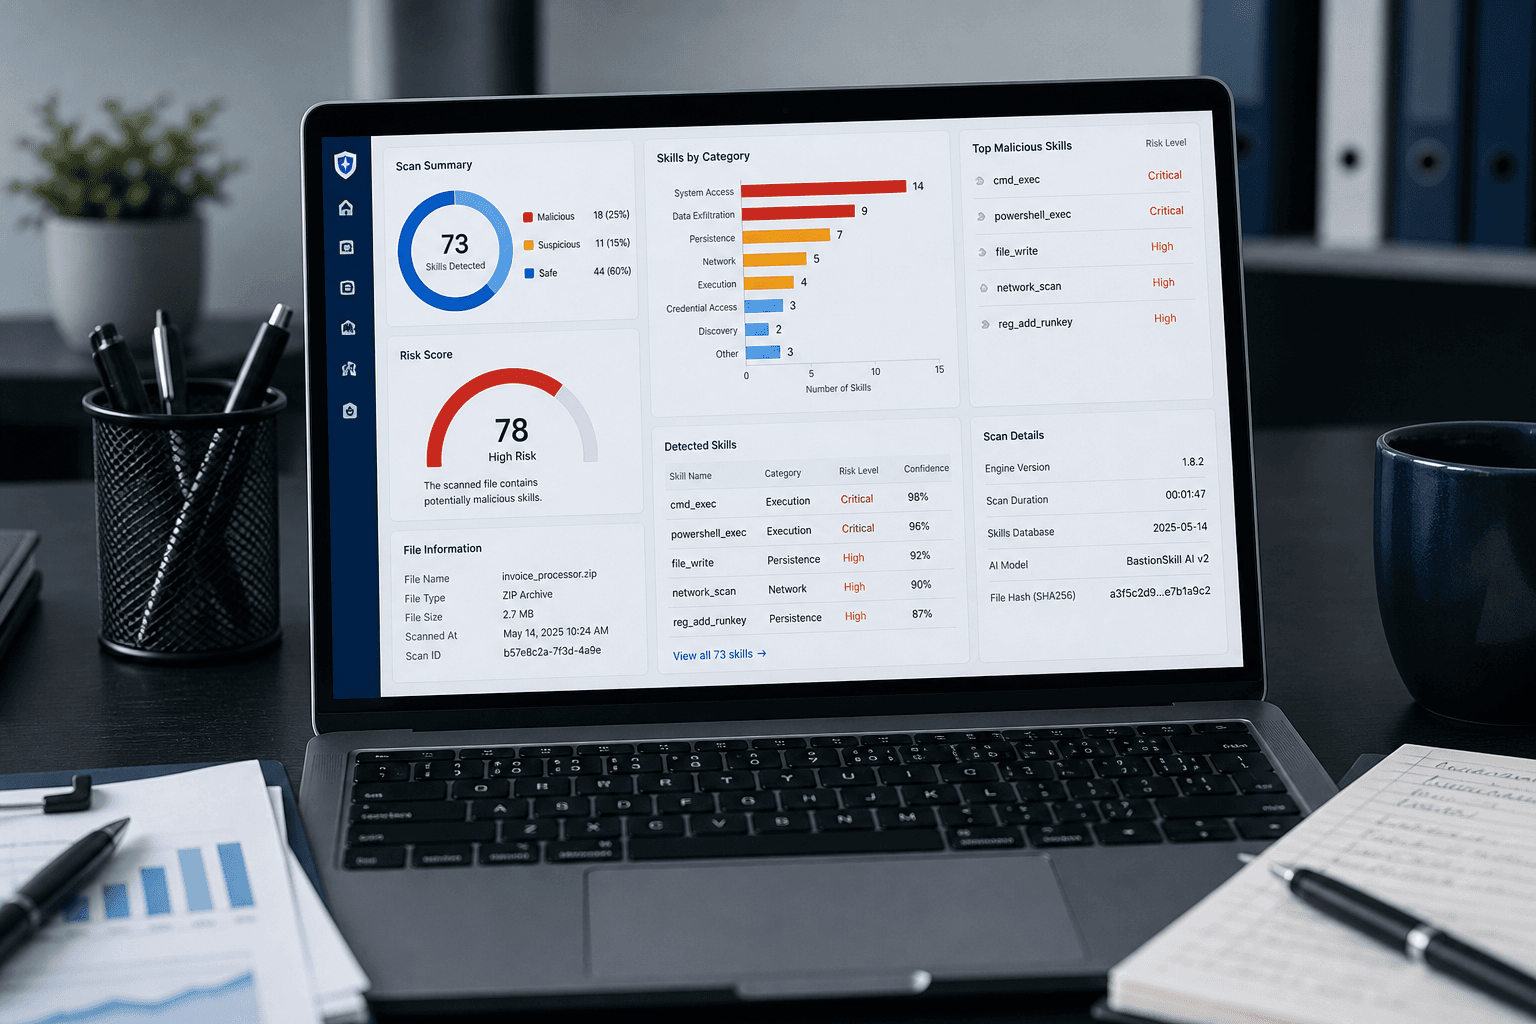
It's a scanner for AI agent skills. When you grab a skill from somewhere other than your own team, Bastionskill checks the code and instructions for red flags. Think of it as a linting step, but for trust. The creator posted it directly to Hacker News, which means it's developer-focused and early-stage, but the direction is clear: treat agent skills like executable code, because they essentially are.
Why do AI agent skills need scanning?
Because a skill isn't just text. It's a bundle of instructions and code that an agent will act on with real permissions. Malicious or sloppy skills could exfiltrate data, run unauthorized commands, or manipulate the agent into doing something its user never asked for. The community is starting to read this as a supply chain moment for AI — not the first, and probably not the last.
What does this mean for AI security?
This looks like the beginning of a security tooling layer for agent ecosystems. If agents become the new app store, someone has to play gatekeeper. Bastionskill is a small, focused entry into that role, and the reaction on Hacker News suggests developers are paying attention. Not a finished product, but a signal that skill-level scrutiny is becoming a real category.